This guide is educational, not personalized financial, legal or security advice. A checklist reduces avoidable mistakes; it cannot make a transaction risk-free.
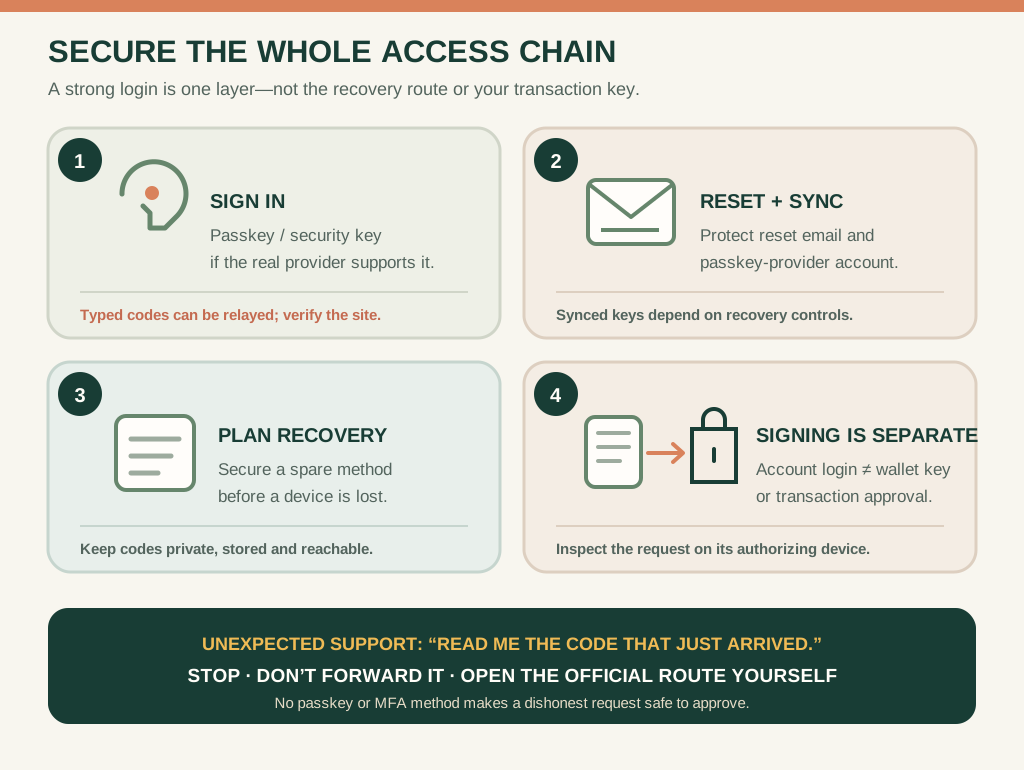
Passkeys and MFA protect account sign-in, not every recovery channel or transaction. Check the actual service's recovery rules and never forward a login code to another person.
- Choose a phishing-resistant passkey or security key when the verified provider supports it; understand any authenticator or SMS fallback.
- Protect the email or account that controls password reset and synced-passkey recovery.
- Store a spare recovery method safely and test it through the provider's official settings before relying on it.
- Keep exchange login separate from wallet signing authority; inspect transaction details on the authorizing device.
A caller asks you to read the login code that just arrived. Which layer are they trying to bypass, and what independently verified route should you use instead?
A passkey is not just another code
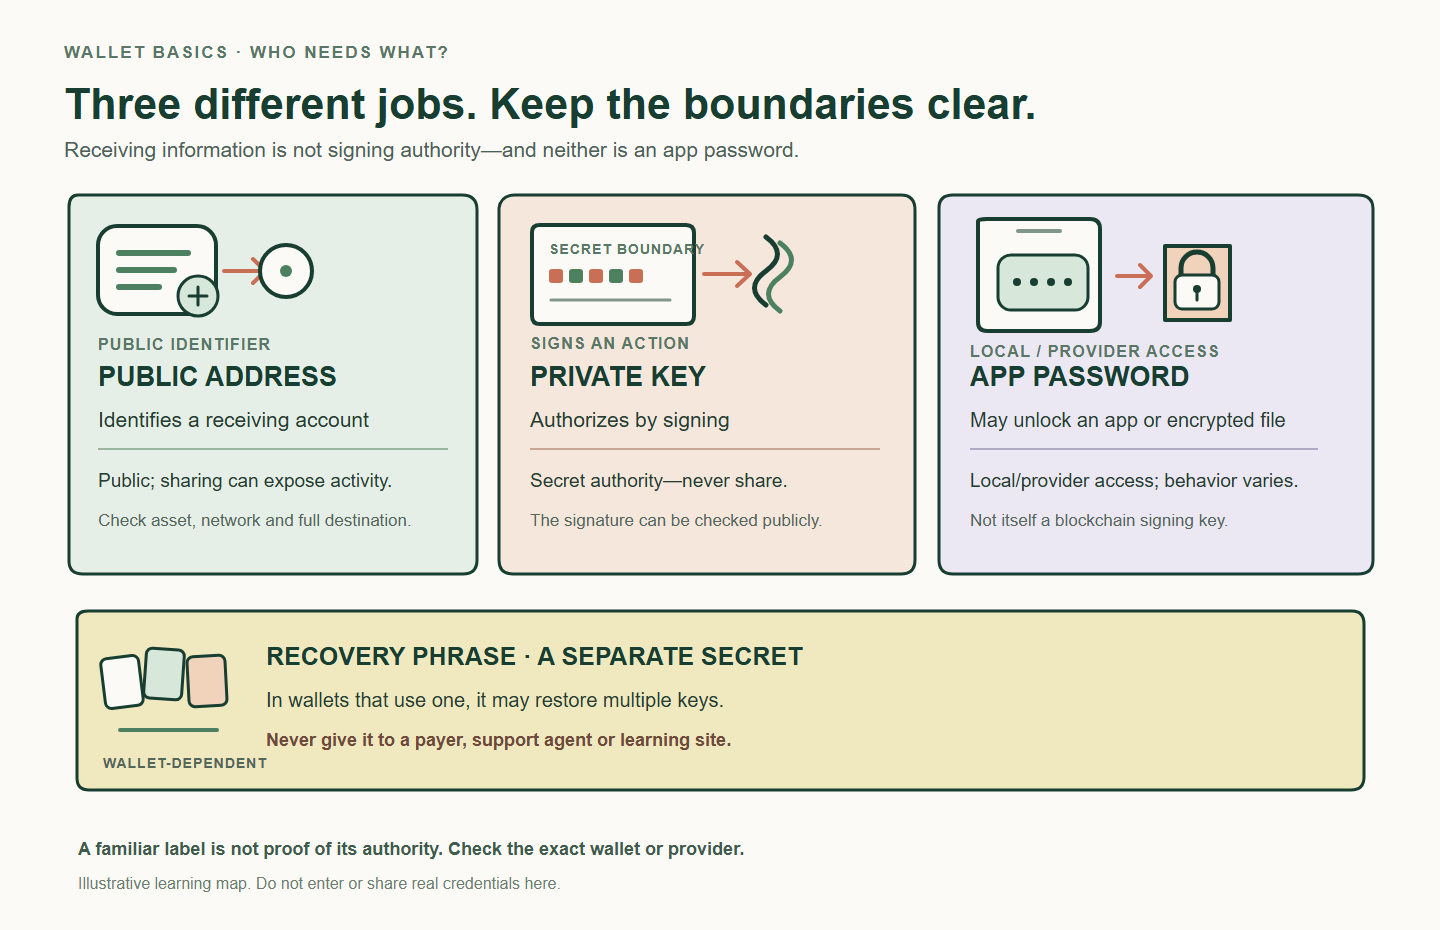
Two-factor authentication uses two different kinds of proof; multi-factor authentication is the broader term. An authenticator app or text can provide a one-time code alongside a password. A passkey is a cryptographic sign-in credential and may replace the password rather than simply add a second box to fill in. What counts as a factor depends on how the service and device implement the login.
Passkeys use public-key cryptography. NIST describes WebAuthn's site-name binding as a way to stop an authenticator response from being reused at an impostor website; a manually typed one-time code is not bound to that site and may be relayed. This is why a passkey or security key is a strong choice when the real provider supports it. An authenticator app can be a useful fallback; SMS relies on the phone-number account and carrier. These options are not interchangeable, and no method removes the need to verify where you are signing in. See NIST's authenticator guidance and the FTC's account-security overview.
Passkeys may sync across devices through a passkey provider, or be bound to one device or security key. Sync can make device replacement easier; it also makes the provider account and its recovery process part of the protection chain. Check how the service you use stores and restores passkeys. Do not assume that deleting an app, changing phones, or resetting an email account has the same effect for every provider. FIDO's passkey overview explains both synced and device-bound passkeys.
Protect the recovery route too
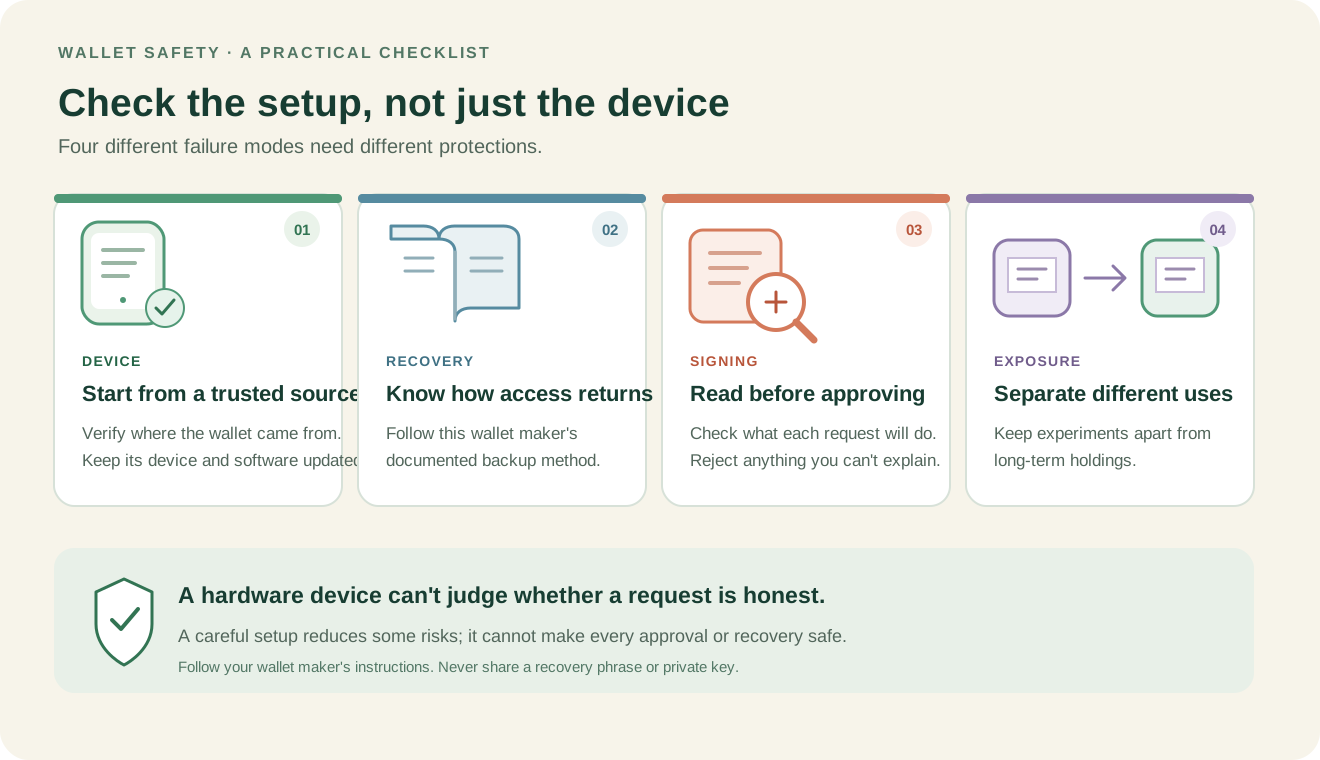
Secure the email or provider account used to reset access with its own strong sign-in. Read the provider's recovery instructions before storing funds. Keep any recovery codes or spare security key somewhere protected but available if your phone is lost; never send a code to a caller, chat, or person claiming to be support. Enter a code only into the sign-in or recovery flow you opened through a verified provider route. The FTC warns that a person asking you to share a verification code may use it to access your account.
Review active sessions, registered devices and API permissions after setup. If the service allows more than one sign-in method, add and test a backup through its official settings before you depend on it. Avoid testing recovery by intentionally locking yourself out.
Login access is not transaction approval
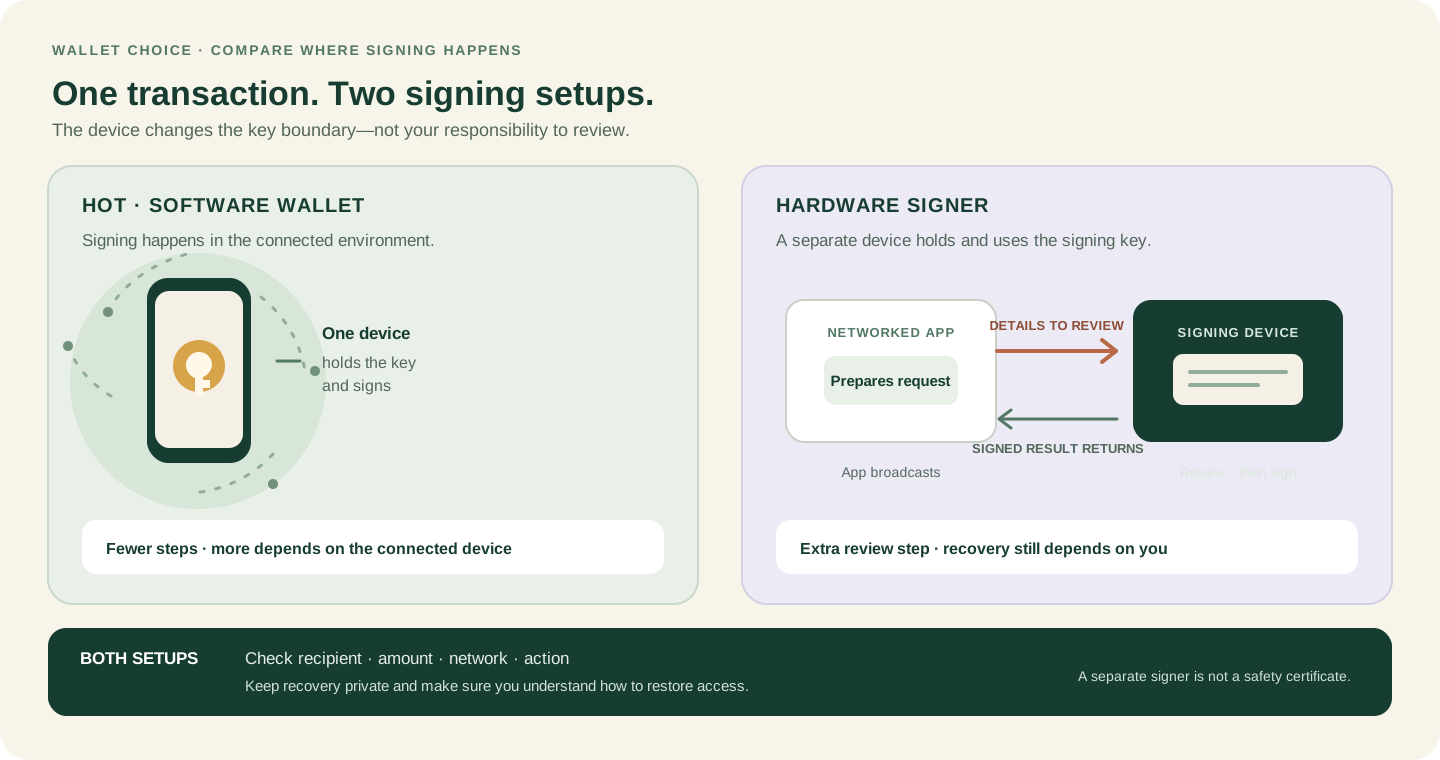
A passkey or MFA protects a service account's login path. It does not decide whether a withdrawal or trade request is honest, and it does not protect a recovery phrase or private key that is already exposed. A self-custody wallet's signing authority is separate from an exchange login. Review the transaction on the device that will authorize it, and learn how Bitcoin wallet custody works without entering any secret into this exercise.
Imagine a message saying “support needs the code that just arrived.” Stop; do not read or forward the code. Open the provider's app or a saved address you verified yourself, check account activity, and contact support through that route. Write a recovery plan that names the account, recovery channel, backup method and device-loss steps—but do not put passwords, one-time codes, recovery phrases or private keys in the plan. StonkBuilder Learn will never need those secrets or a wallet connection.
Check your understanding.
Should support receive your one-time login code in a surprise call?
A correct answer records local learning progress, not a qualification or proof of financial readiness.
Put this lesson in context
Start with who controls the keys. Continue to recovery and backup planning before connecting an application.
Sources & context
- National Institute of Standards and Technology — Digital Identity Guidelines: Authentication and Authenticator Management ↗Consulted 2026-10-05
- FIDO Alliance — FIDO Passkeys ↗Consulted 2026-10-05
- US Federal Trade Commission — Use Two-Factor Authentication To Protect Your Accounts ↗Consulted 2026-10-09
Original educational content prepared for this project. Sources provide context, not endorsement or a guarantee that every statement remains current. Rules, product interfaces and availability can change.
Keep learning in Telegram.
Open this published guide in the learning bot. No account connection or wallet is needed.
Join the $STONKB community.
Follow project updates, share useful ideas and meet other builders. You do not need to buy $STONKB to join.
Take what you learned.
Leave the pressure behind.