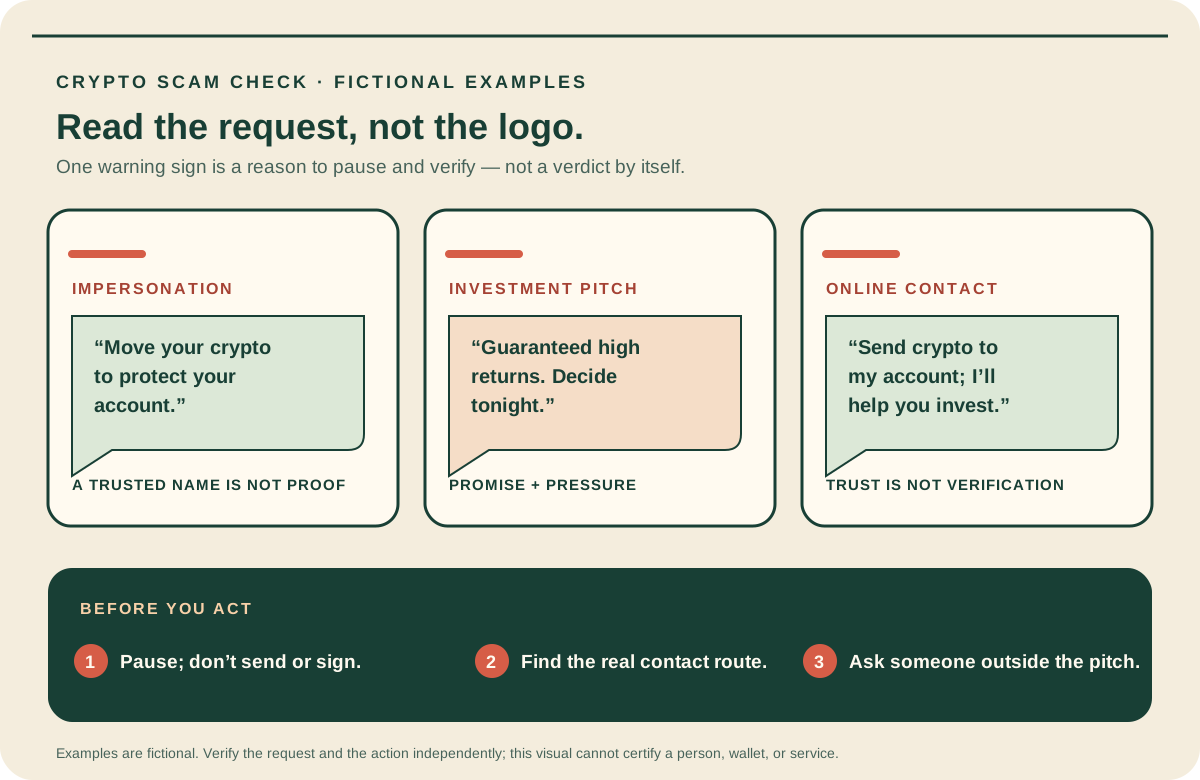
This guide is educational, not personalized financial, legal or security advice. A checklist reduces avoidable mistakes; it cannot make a transaction risk-free.
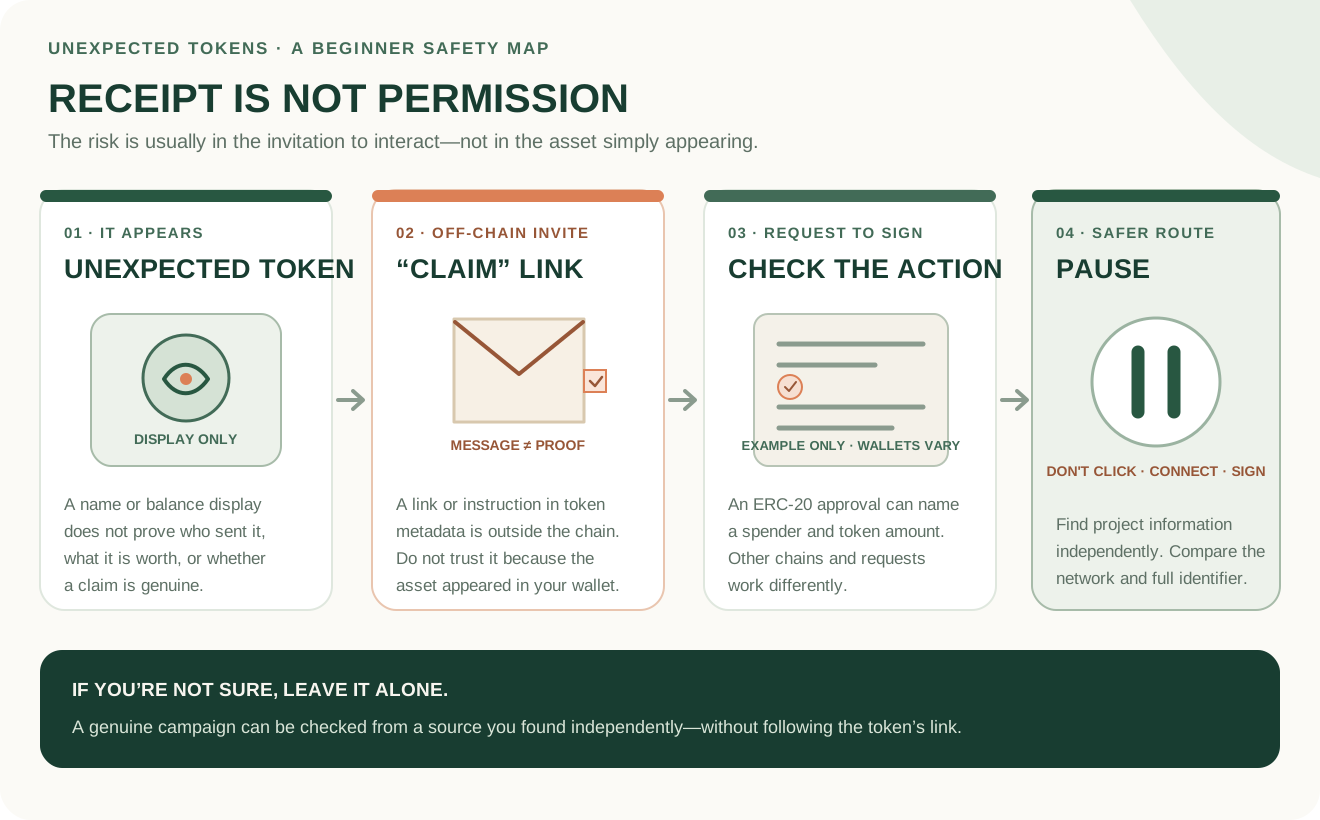
An asset appearing is not independent proof of its issuer or claim link. A signature request can have different effects across networks.
- A token can appear without your choosing it; its display does not prove the issuer, value or claim.
- A message or URL in token metadata is off-chain content, not a verified invitation.
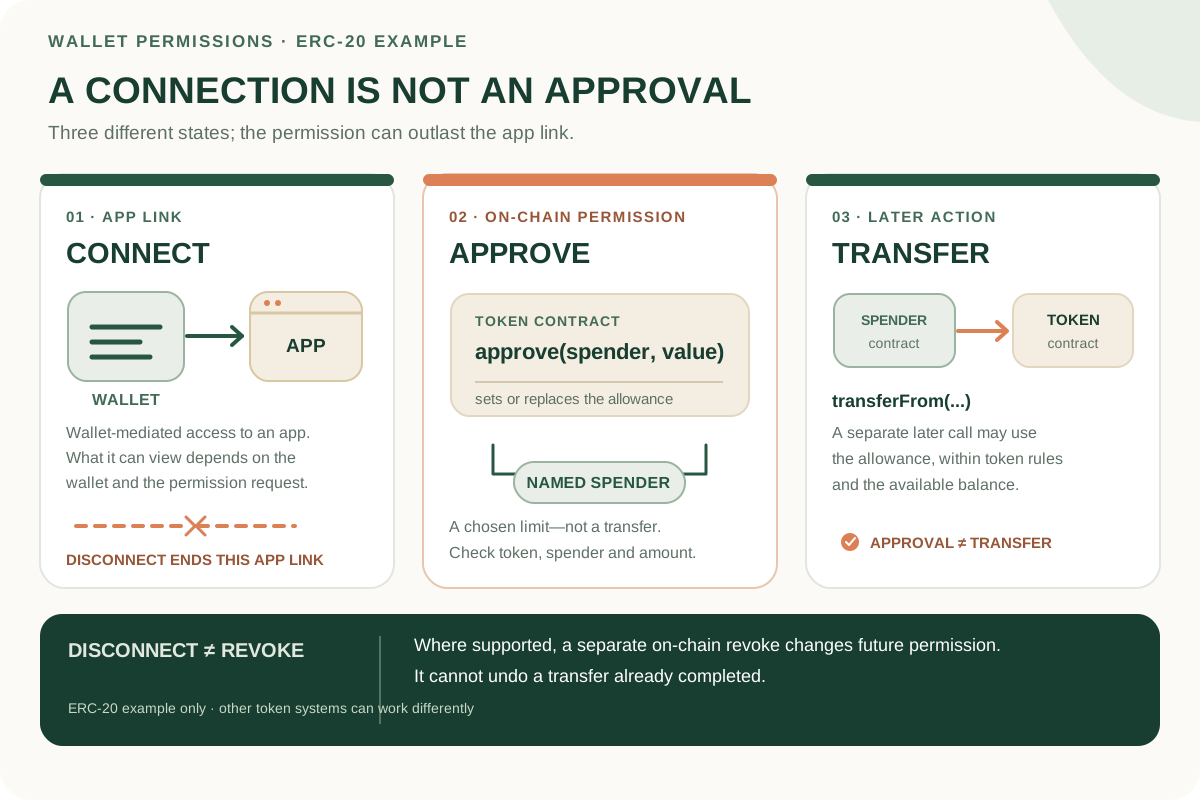
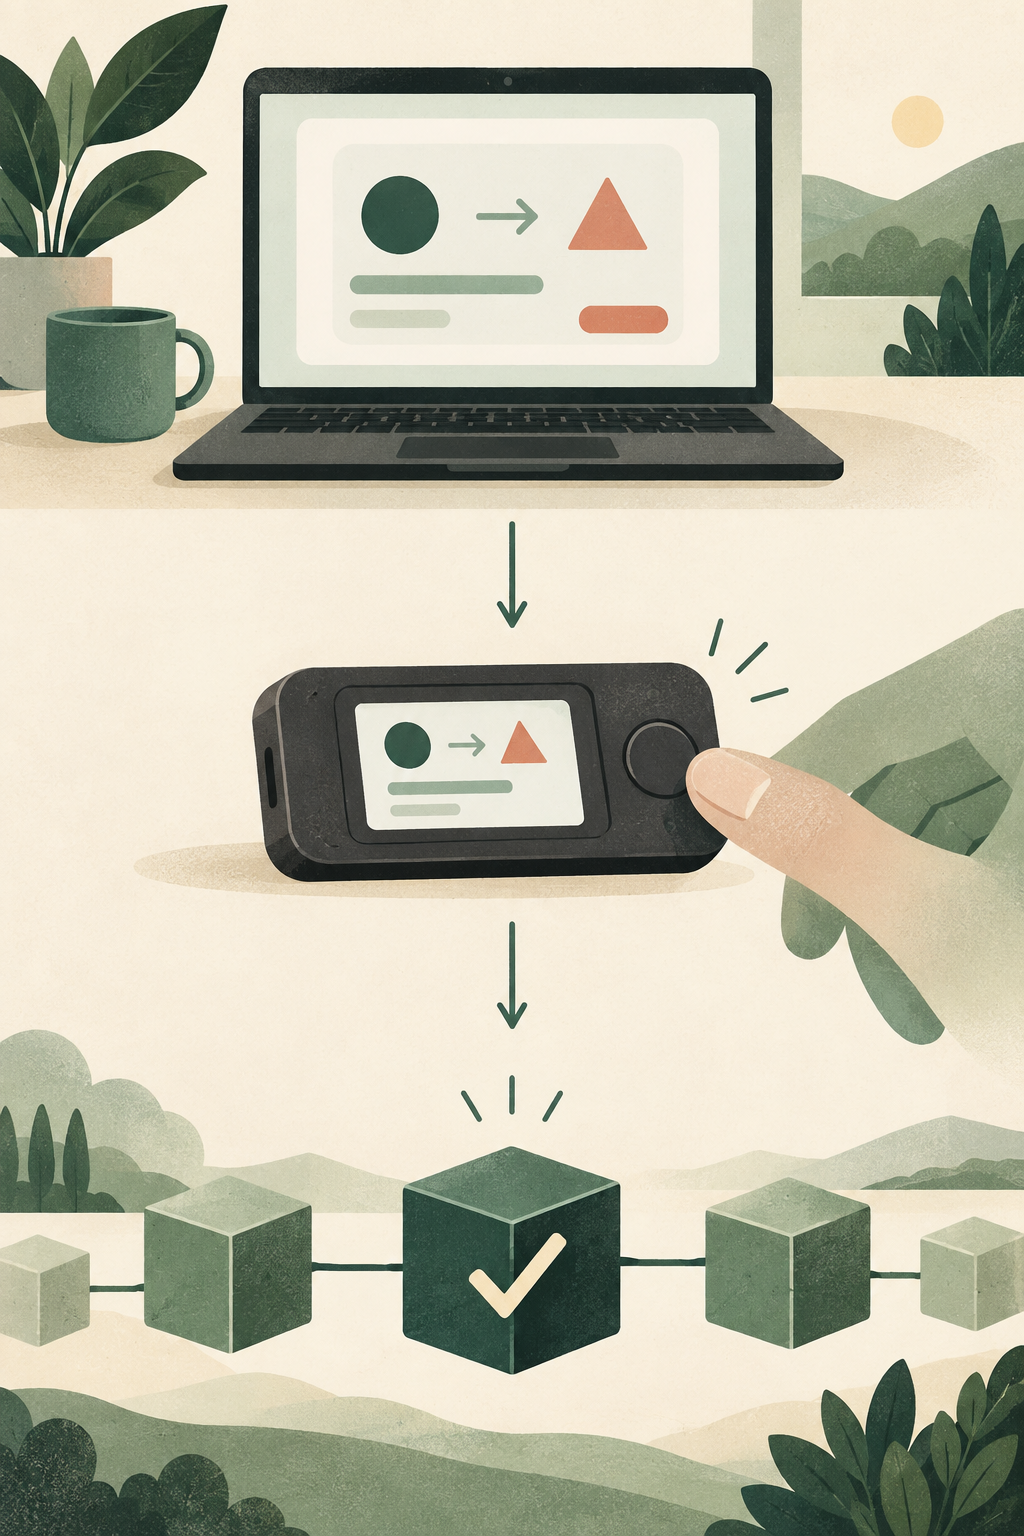
- Inspect the exact signing request and network. ERC-20 approvals name a spender and amount; other networks and requests differ.
- If unsure, do not click, connect or sign. Find project information independently and compare the full token identifier.
An unexpected token advertises a valuable claim. What can you verify without using its link or signing a request?
Receipt is not an invitation
A token can appear in a public address because someone sent it there. That does not prove endorsement, eligibility, a real prize or saleable value. A name, image, or wallet display is not independent evidence of who issued it. The FTC warns that promises of free cryptocurrency can be a scam; that warning is not proof that every unsolicited token is fraudulent.
The risk is usually in an invitation to interact, not in the token merely appearing. An unsolicited NFT may include a claim link or message that leads to phishing or a malicious signing request, as MetaMask's NFT airdrop guidance explains. On Ethereum, an ERC-20 approve request authorizes a named spender to use up to a specified amount of that token; the ERC-20 standard defines this allowance. Other networks and wallet requests work differently. Never infer what a signing request will do from the token's name, image or displayed value.
How the trap works
An unfamiliar token shows a large dollar estimate and tells you to redeem it on a website. A displayed estimate is not proof that you can sell the asset or withdraw value. Its “claim” button may lead to a wallet connection and then ask for an ERC-20 allowance or a different transaction. The exact action depends on the selected network and the request shown by the wallet—not on the token's appearance.
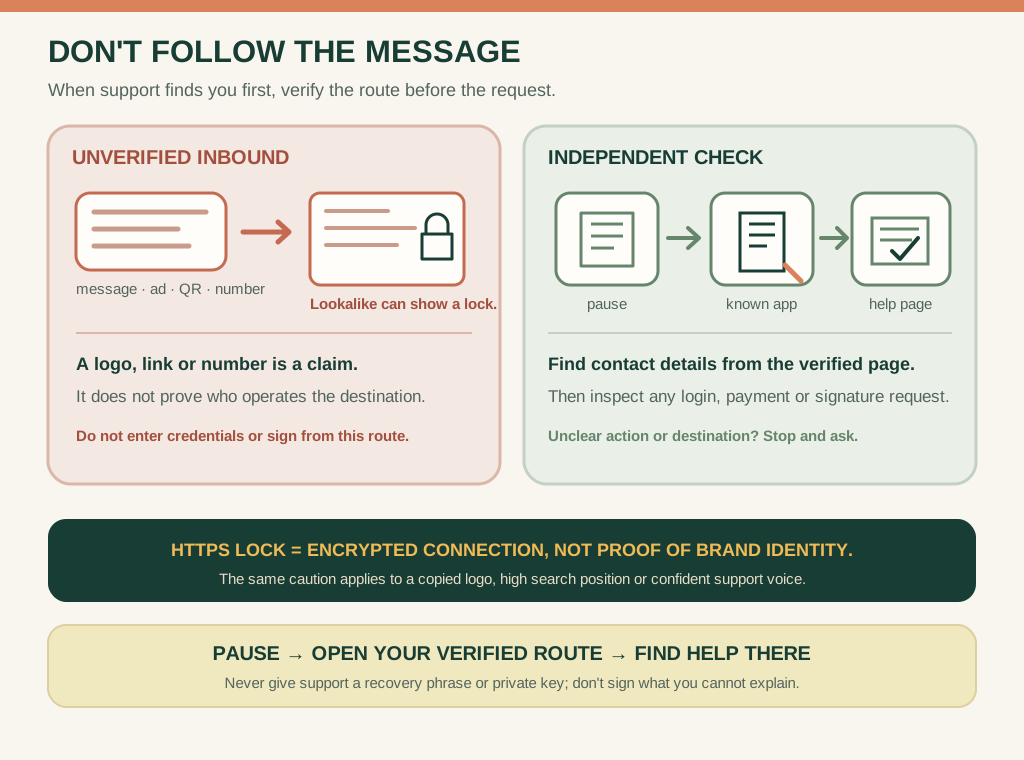
Pause before clicking, connecting or signing. If a campaign might be genuine, find the project channel independently, then compare the exact network, contract or mint, and eligibility rules. The Ethereum security guide describes airdrop lures on Ethereum; it is one network-specific example, not a universal transaction model.
A closer check
The safest first move is to leave the unexpected asset alone. Do not click, connect, approve, swap, claim, move or burn it just because its metadata tells you to. If you need to investigate, start from information you find independently and inspect the network and complete token identifier there. Use a wallet's documented hide or report controls only when that wallet provides them.
If you already interacted
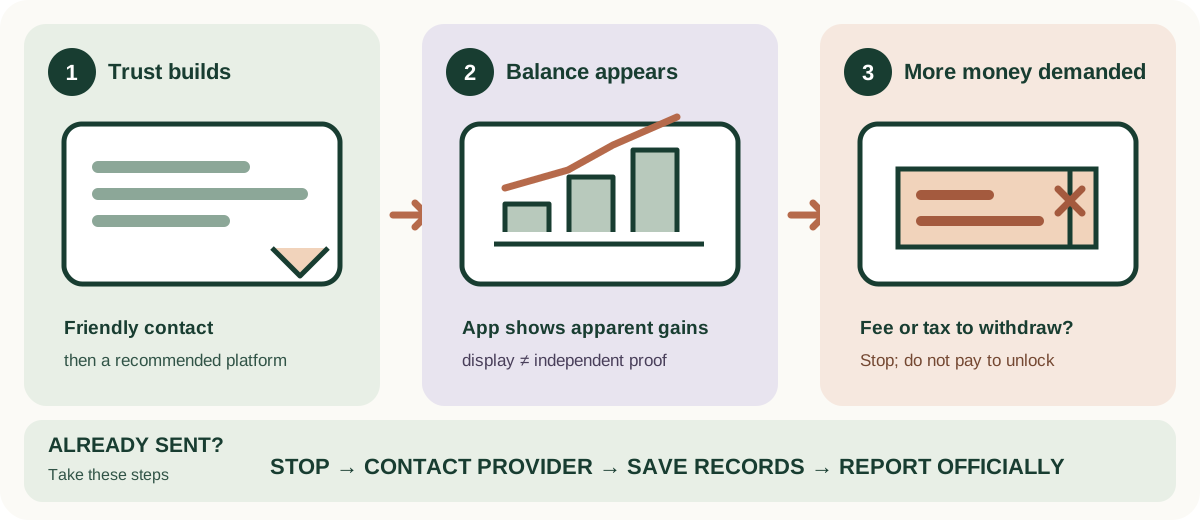
Stop signing. Keep non-sensitive details such as the network, token identifier, site address and transaction record; never share a recovery phrase, private key, password or signing code. Use the affected wallet or network's official incident guidance, and do not pay a stranger to unlock or recover the balance. For the permission distinction, read token approvals explained and phishing links and fake support.
Check your understanding.
Does receiving a token mean its claim link is safe?
A correct answer records local learning progress, not a qualification or proof of financial readiness.
Put this lesson in context
Use these guides to recognize suspicious requests and decide which safety question to ask next.
Sources & context
- US Federal Trade Commission — Cryptocurrency and scams ↗Consulted 2026-10-09
- ethereum.org — Security and scam prevention ↗Consulted 2026-10-11
- Ethereum Improvement Proposals — ERC-20: Token Standard ↗Consulted 2026-10-05
- MetaMask Help Center — NFT airdrop scams ↗Consulted 2026-10-05
Original educational content prepared for this project. Sources provide context, not endorsement or a guarantee that every statement remains current. Rules, product interfaces and availability can change.
Keep learning in Telegram.
Open this published guide in the learning bot. No account connection or wallet is needed.
Join the $STONKB community.
Follow project updates, share useful ideas and meet other builders. You do not need to buy $STONKB to join.
Take what you learned.
Leave the pressure behind.