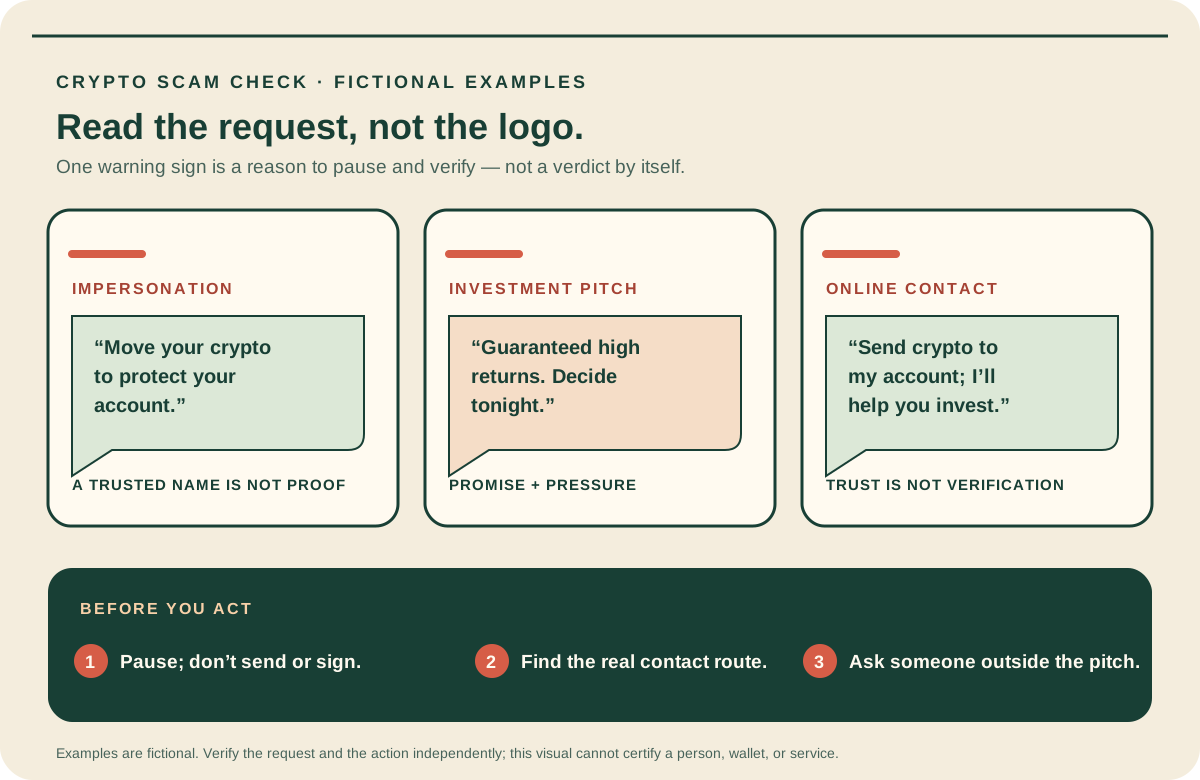
This guide is educational, not personalized financial, legal or security advice. A checklist reduces avoidable mistakes; it cannot make a transaction risk-free.
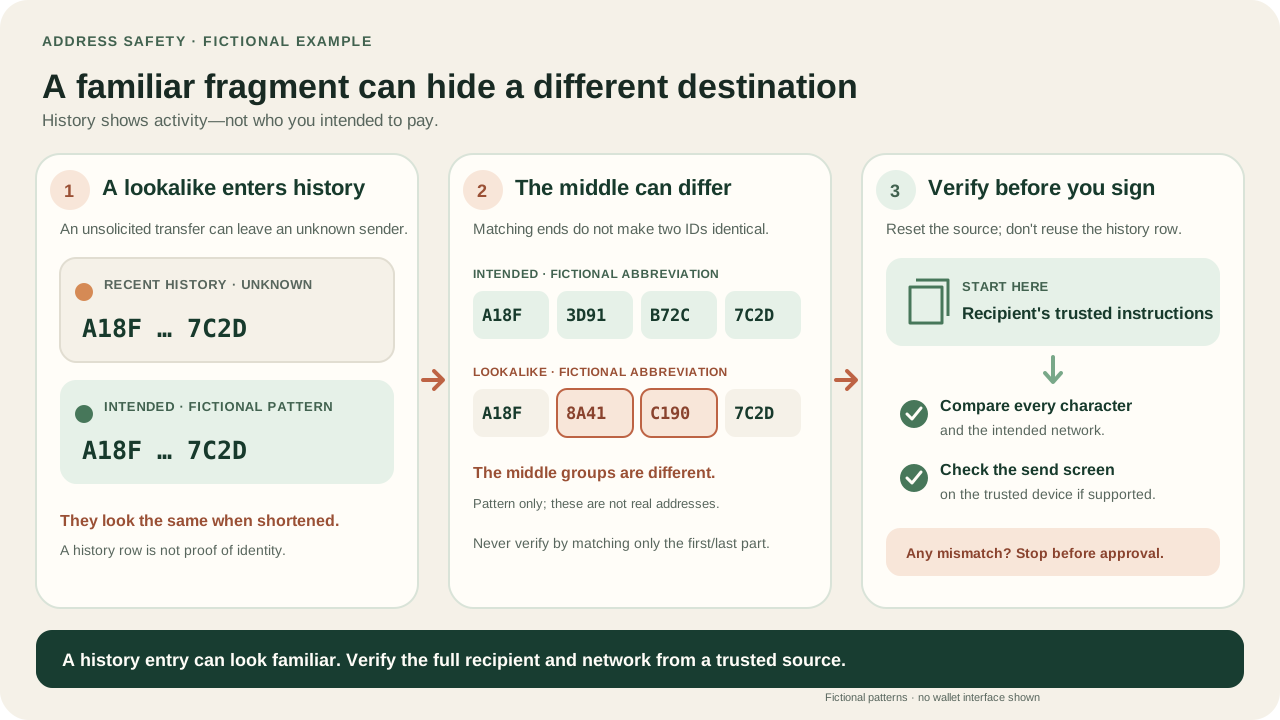
Transaction history shows activity, not identity. The abbreviated strings are fictional; verify the complete destination and network independently.
- An unsolicited small or zero-value token transfer can leave a lookalike address in recent history.
- Matching visible beginnings and endings do not prove the full identifiers match; the fictional example differs in the middle.
- Start from independently verified recipient instructions, then check every address character and the network before signing.
- A wallet warning can be an extra signal, but protections vary and do not replace the independent check.
Two fictional history rows look alike when shortened. Name the independent source, full-address comparison, and network check you would use before approving.
How address poisoning exploits attention
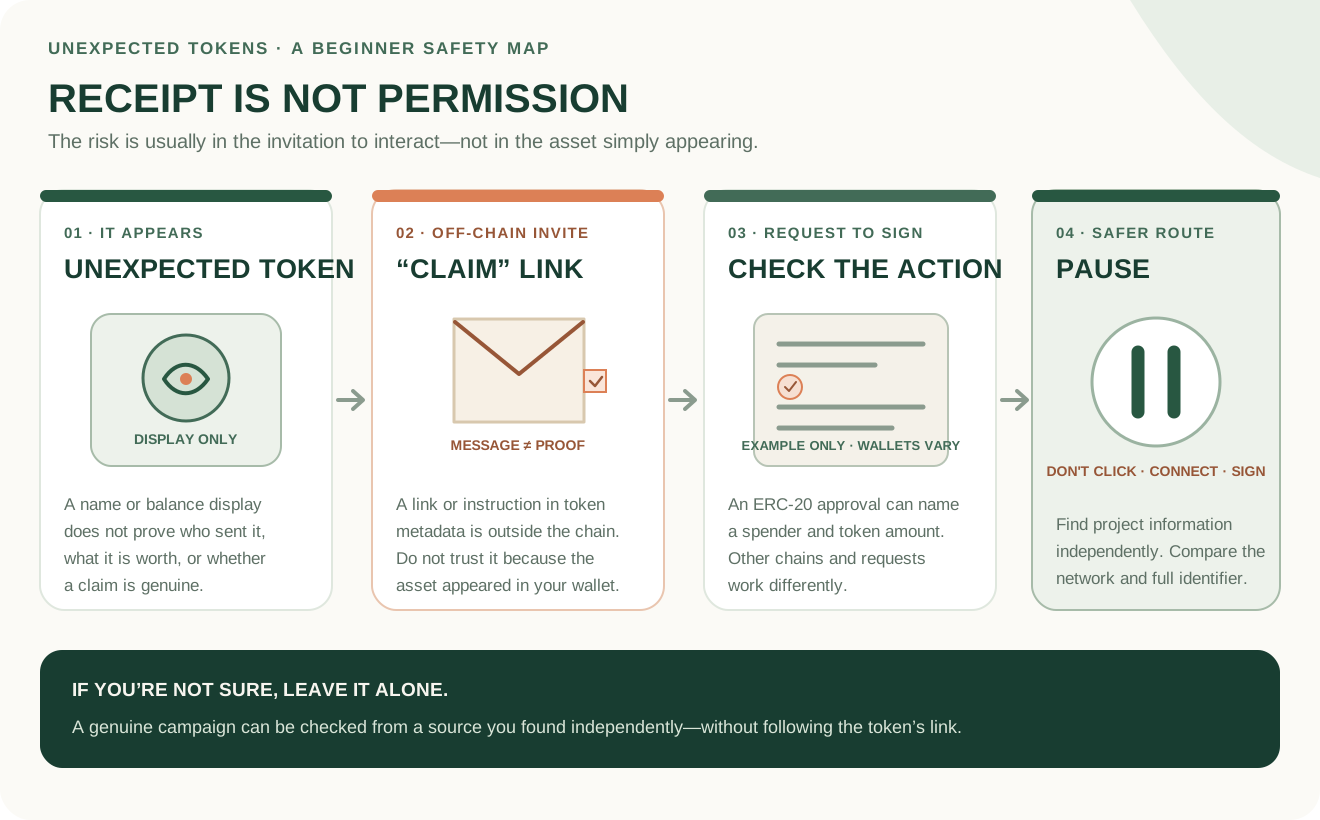
Address poisoning is a social-engineering tactic built around transaction history. An attacker can send a tiny or zero-value token transfer from a lookalike address, leaving it in a wallet or explorer history. Because some interfaces shorten long identifiers, a user may copy a recent sender after recognizing only matching beginning and ending characters, then send funds to the attacker by mistake. The incoming transfer is bait—not evidence that the sender is a supplier, friend or service you intended to use.
The chain can show that an address participated in a transaction. It cannot tell you that the address belongs to the person named in your notes. Identity and destination verification remain separate from on-chain history.
A safer recipient workflow
Start from the recipient's independently verified instructions, not from a recent history row. Compare the complete address and network on the send screen and, where supported, on the trusted device display. Some wallets may flag a suspected lookalike, but protections vary and cannot replace checking the full destination and network yourself. If a recipient changes its instructions, confirm the change through a second channel you already trust. Address books help only when the saved entry was verified at the time it was created.
Do not let a previous successful test replace a fresh check. Wallets, exchanges and applications can present different network labels, and a matching prefix or suffix is not a full match.
A short scenario
A supplier's genuine address begins and ends with the same characters as a poisoned address in your history. The wallet shows only those fragments. Copying the history entry sends the payment to the attacker; the explorer then records a real transaction, but not the business relationship you intended. The control that mattered was verifying the complete destination before signing.
If the check fails
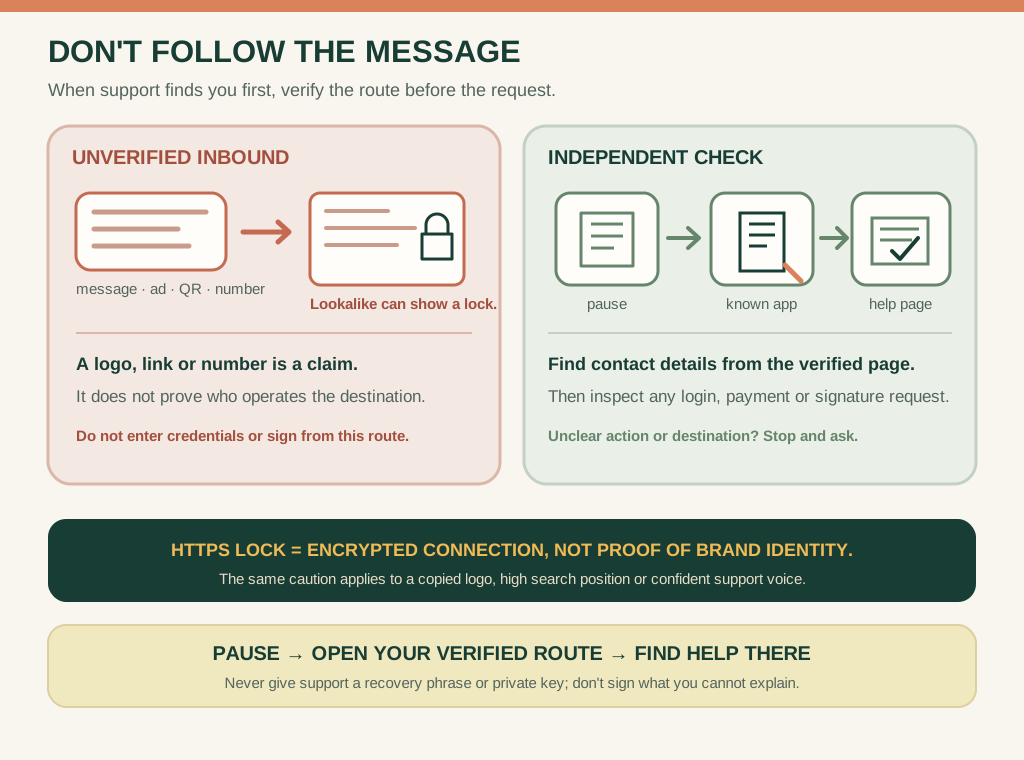
Stop before approval. Capture non-sensitive evidence, ask the intended recipient to confirm its address through a trusted route and use official support if funds or credentials may already be exposed. Ignore anyone who contacts you privately with a guaranteed recovery offer. For a related signing risk, read blind signing and message signatures.
Check your understanding.
Is a recent transaction sender a verified payment destination?
A correct answer records local learning progress, not a qualification or proof of financial readiness.
Put this lesson in context
Use these guides to recognize suspicious requests and decide which safety question to ask next.
Sources & context
- US Federal Trade Commission — Cryptocurrency and scams ↗Consulted 2026-10-09
- ethereum.org — Security and scam prevention ↗Consulted 2026-10-11
- MetaMask Help Center — Address poisoning scams ↗Consulted 2026-10-02
Original educational content prepared for this project. Sources provide context, not endorsement or a guarantee that every statement remains current. Rules, product interfaces and availability can change.
Keep learning in Telegram.
Open this published guide in the learning bot. No account connection or wallet is needed.
Join the $STONKB community.
Follow project updates, share useful ideas and meet other builders. You do not need to buy $STONKB to join.
Take what you learned.
Leave the pressure behind.