This guide is educational, not personalized financial, legal or security advice. A checklist reduces avoidable mistakes; it cannot make a transaction risk-free.
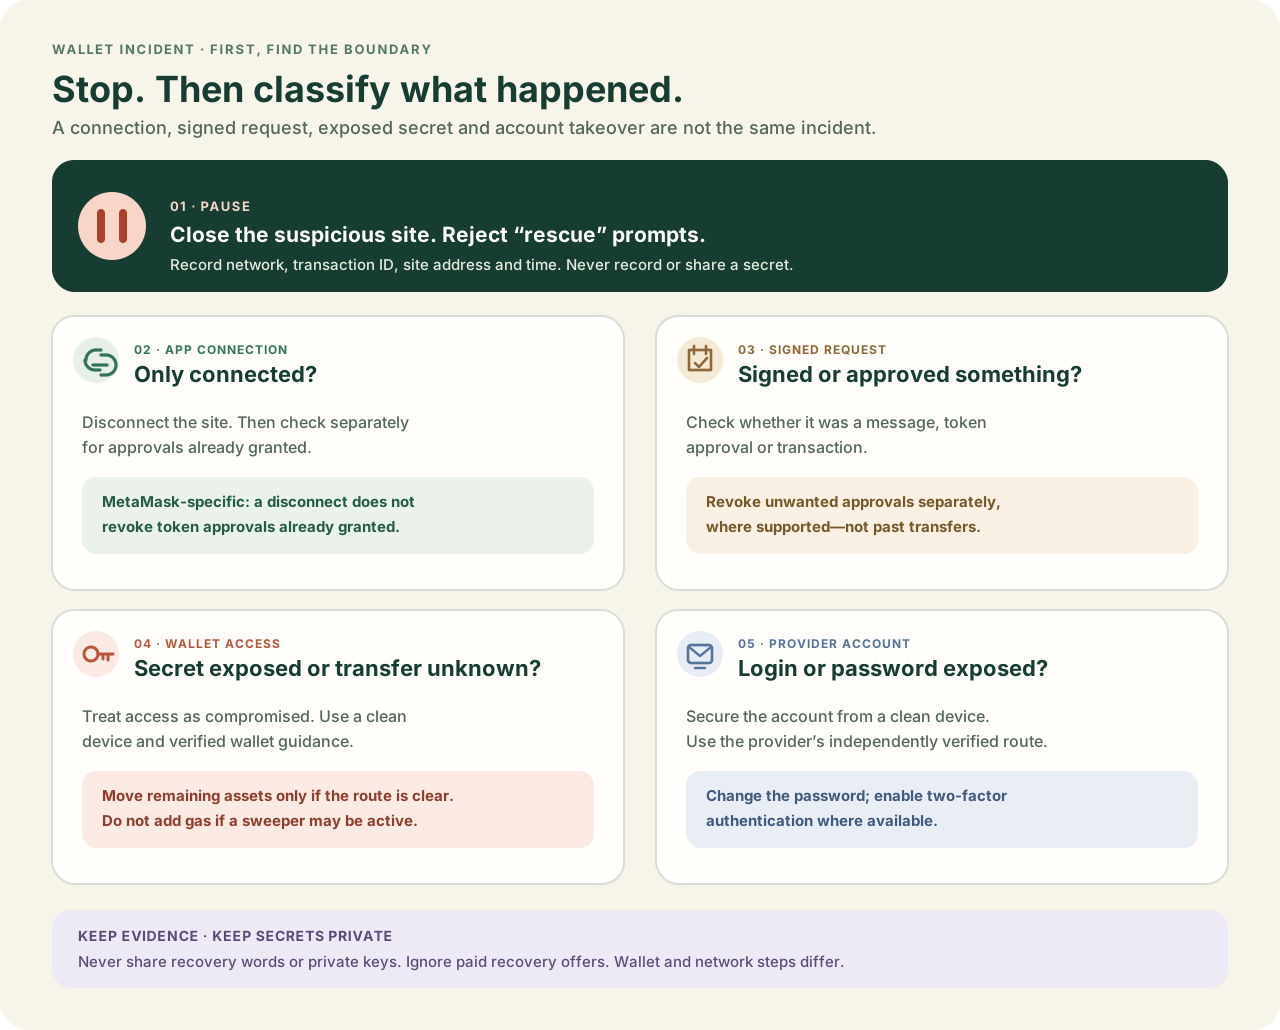
A response map, not a diagnosis. Message signatures, token approvals, on-chain transactions and exposed keys are different events; options vary by wallet and network. Never share a recovery phrase or private key, and do not pay an unsolicited recovery agent.
- Stop using the suspicious site and reject rescue prompts. Save the network, transaction ID, site address and time—but never a secret.
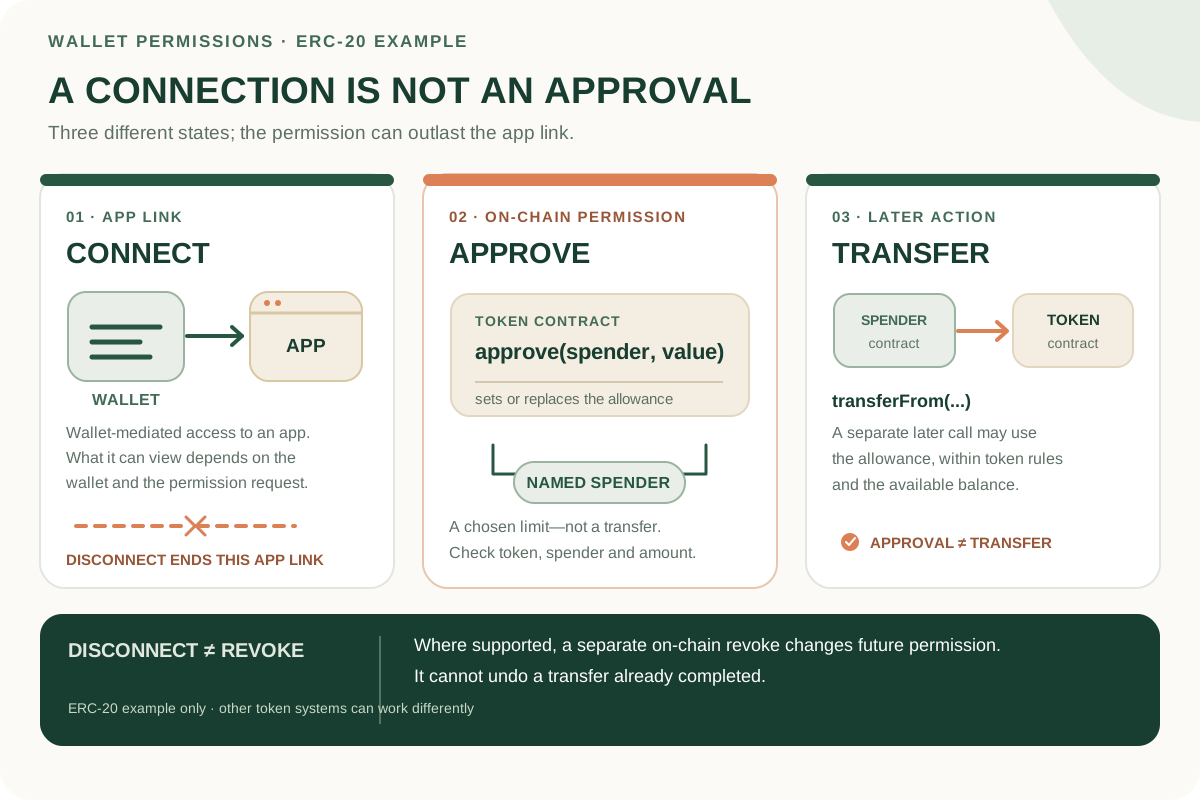
- If you only connected, disconnect the site and check separately for earlier approvals; a MetaMask dapp disconnect does not revoke token approvals.
- If you signed something, determine whether it was a message, token approval or transaction. Revoke unwanted approvals separately where supported; that cannot undo an earlier transfer.
- If a recovery phrase or private key was exposed, or transfers are unexplained, treat wallet access as compromised. Use a clean device and verified wallet guidance; move remaining assets only if the transaction is understood.
- If an exchange or sign-in account was exposed, secure it from a clean device and contact the provider through its independently verified support route.
Without connecting a wallet or moving funds, classify four fictional reports: a site was connected; a token approval was signed; a recovery phrase was shared; an exchange password was exposed. Which response differs in each case?
Stop the interaction and classify the exposure
If a wallet or account may be compromised, stop using the suspicious site and reject new “rescue” prompts. Write down what happened without exposing secrets: did you only connect, sign a message, grant an approval, approve a transaction, disclose a private key or reveal a recovery phrase? These are different incidents and need different responses.
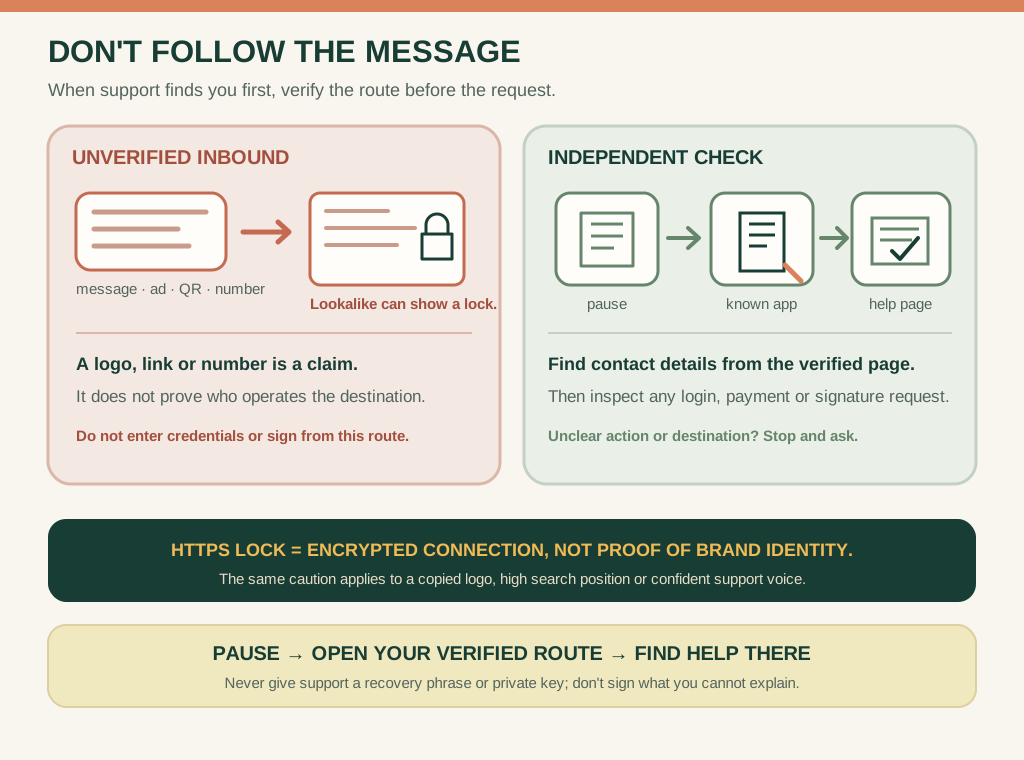
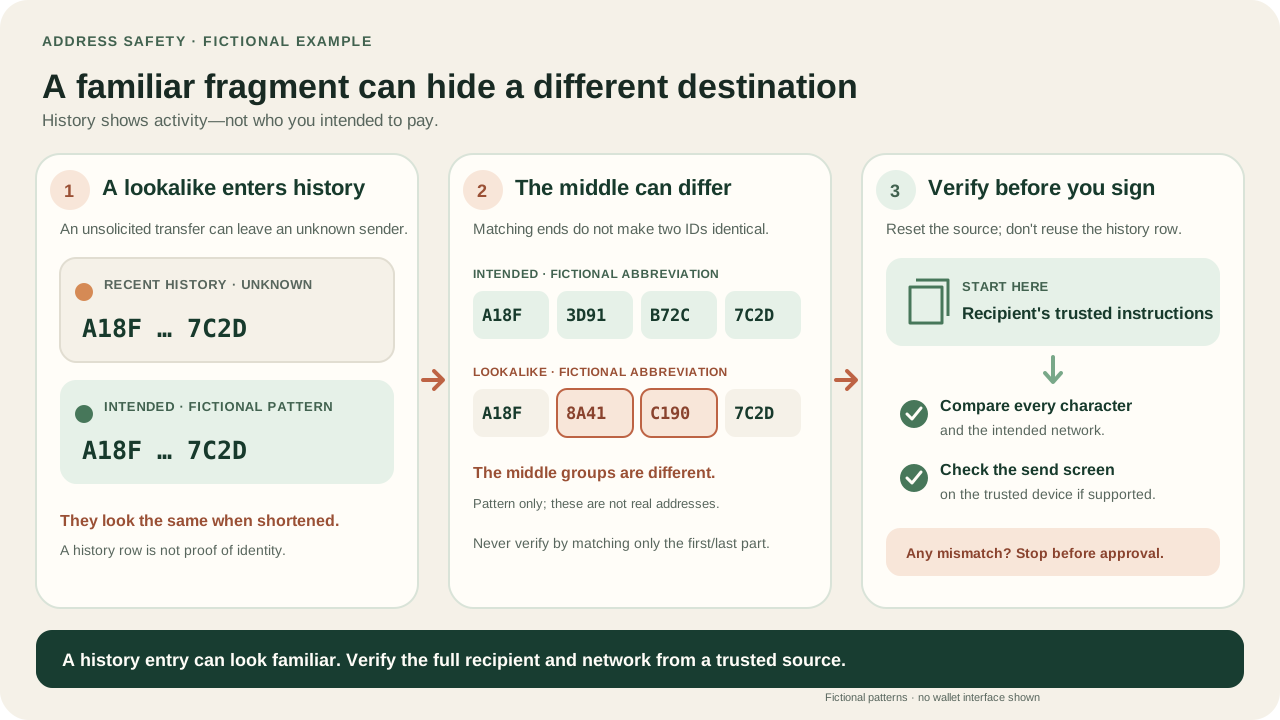
Preserve transaction IDs, domains, wallet addresses and non-sensitive screenshots. Use the wallet maker, exchange or network's official support route reached independently. Do not continue the conversation with the person who sent the suspicious link.
The response depends on the boundary crossed
A connection alone is not the same as a signed permission. Revoking a harmful approval may limit future use, but it cannot return funds already transferred. Changing an app password does not repair an exposed signing key or recovery phrase. If the underlying authorization is exposed, remaining assets may need to move to a newly secured setup; do not improvise when a sweeper, contract position, missing fee asset or complex account model makes the transfer unsafe.
A wallet-specific example matters: MetaMask's dapp guide says disconnecting a dapp does not revoke token approvals already granted. Check approvals separately through the wallet's trusted tools; disconnecting is not a substitute for revocation. Other wallets and networks may work differently.
Avoid adding funds to a compromised wallet simply to pay a fee until qualified, independently verified help has assessed the situation. An attacker may be watching for the deposit.
A closer check
If compromise is possible, prioritize containment over investigation. Use a known-clean device to move remaining assets only when the destination and transaction are understood, revoke permissions where the network supports it and document the timeline. Changing one password does not repair an exposed key or reveal every affected account.
What not to do
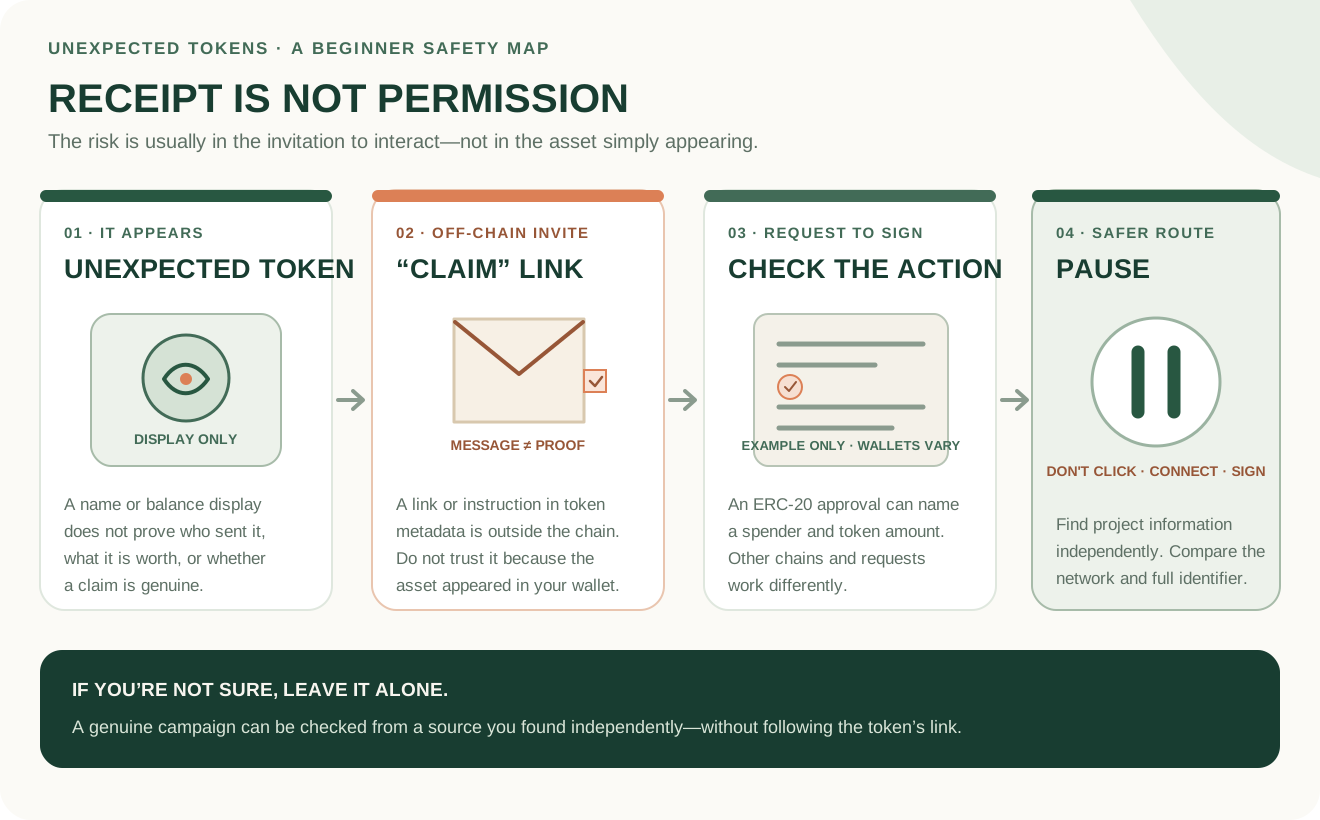
Do not pay an unsolicited recovery agent, share another secret to prove ownership or assume a confirmed transaction can be reversed. Report the incident to the relevant provider and local authorities where appropriate. This guide is a classification aid, not a diagnosis of a live wallet. For the permission boundary, read token approvals explained; for the first route risk, read phishing links, fake support and the bookmark habit.
Check your understanding.
What does revoking an approval not do?
A correct answer records local learning progress, not a qualification or proof of financial readiness.
Put this lesson in context
Use these guides to recognize suspicious requests and decide which safety question to ask next.
Sources & context
- ethereum.org — Security and scam prevention ↗Consulted 2026-10-11
- Bitcoin.org — Securing your wallet ↗Consulted 2026-10-11
- US Federal Trade Commission — What to do if you were scammed ↗Consulted 2026-10-11
- MetaMask Help Center — User guide: dapps ↗Consulted 2026-10-11
- MetaMask Help Center — How to revoke smart contract allowances/token approvals ↗Consulted 2026-10-11
- MetaMask Help Center — I've been hacked or scammed (unauthorized transactions on my account) ↗Consulted 2026-10-11
Original educational content prepared for this project. Sources provide context, not endorsement or a guarantee that every statement remains current. Rules, product interfaces and availability can change.
Keep learning in Telegram.
Open this published guide in the learning bot. No account connection or wallet is needed.
Join the $STONKB community.
Follow project updates, share useful ideas and meet other builders. You do not need to buy $STONKB to join.
Take what you learned.
Leave the pressure behind.